Regulatory alignment
IT regulatory compliance
SEBI, RBI and IRDAI alignment for cybersecurity controls, cloud governance, reporting and audit readiness.
- SEBI CSCRF
- RBI
- IRDAI
- Cloud governance
Regulatory alignment
From compliance pressure to a governed security programme.
Zoffec helps regulated organisations translate cybersecurity requirements into practical controls, governance routines, managed monitoring and audit-ready evidence.
- Every requirement mapped to a control and owner
- Evidence prepared for inspection
- Overlapping rules mapped once
3
Regulators covered
Frameworks
Which rules apply to you.
Applicability depends on your licence and activities. We confirm it during the gap assessment.
- 01
SEBI CSCRF
Applies to
SEBI-regulated entities and market intermediaries
Focus
Cybersecurity and cyber resilience framework
- 02
RBI
Applies to
Banks, NBFCs and other RBI-regulated entities
Focus
IT governance, cybersecurity and outsourcing
- 03
IRDAI
Applies to
Insurers and insurance intermediaries
Focus
Information and cybersecurity guidelines
SEBI CSCRF services
A structured compliance operating model.
Gap assessment
Identify cybersecurity, governance, reporting and evidence gaps against framework requirements.
Compliance strategy
A practical framework, rollout sequence, responsibility map and remediation plan.
Controls implementation
Control rollout, documentation, validation and evidence preparation.
Managed SOC alignment
Monitoring, incident response and reporting aligned with regulatory expectations.
vCISO advisory
Executive oversight for risk decisions, board updates and compliance maturity.
Managed compliance
Ongoing assessments, status dashboards, reporting support and improvement tracking.
Cloud governance
Cloud adoption with regulatory control.
Assess cloud governance, security controls, data handling, business continuity and ongoing evidence requirements.
Cloud gap assessment
Operating model, data locality, ownership, disaster recovery and governance readiness.
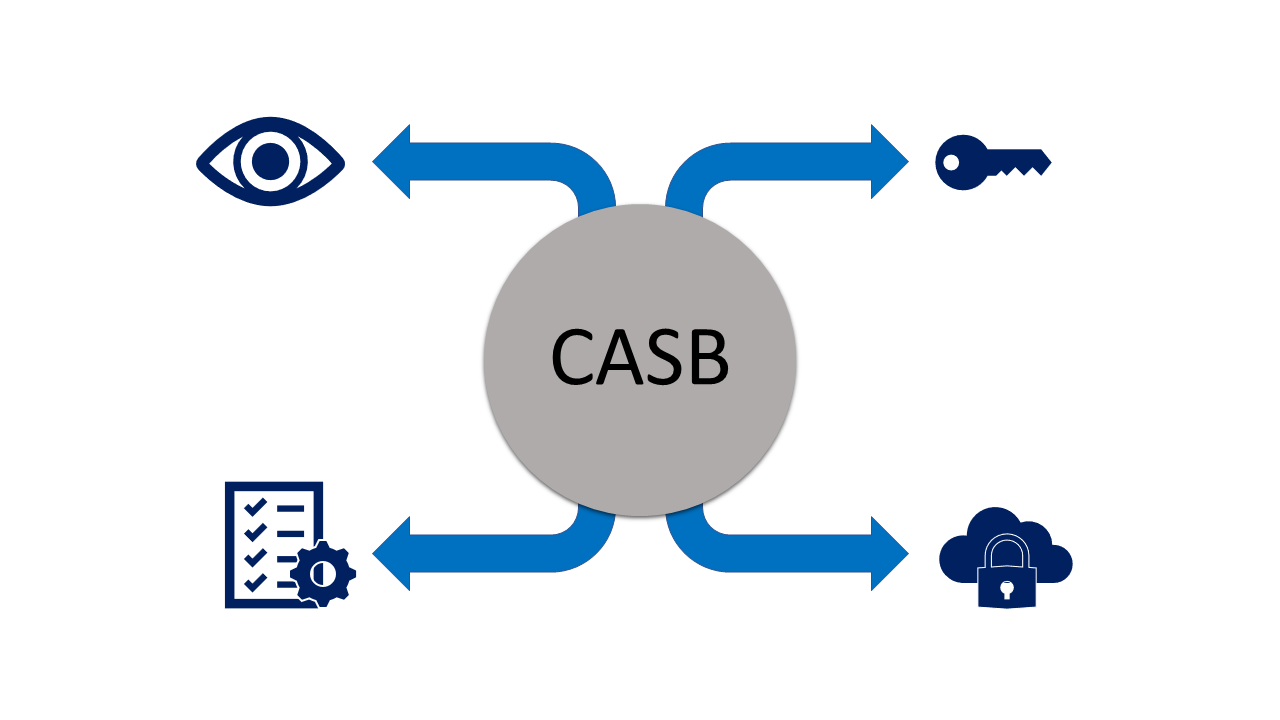
Security control assessment
Cloud controls, policy enforcement, identity, logging and evidence.
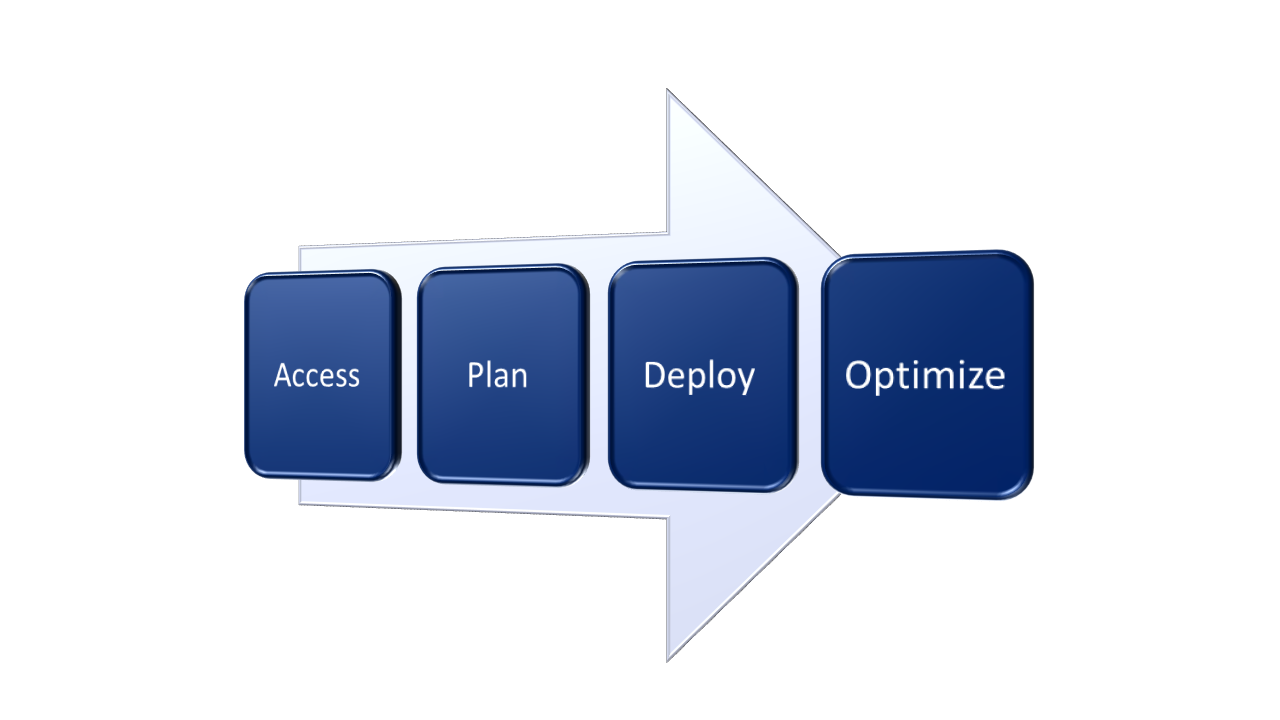
Implementation support
Build the framework and guide teams through control implementation and documentation.
Coverage
What the programme addresses.
- Governance
- Data localisation
- Cybersecurity
- Disaster recovery
- Vendor risk
- Incident reporting
01Does SEBI CSCRF apply to us?
It applies to SEBI-regulated entities, with requirements scaled by category. We confirm your category and obligations in the gap assessment.
02Can you help with an upcoming inspection?
Yes. We prioritise the highest-risk gaps and prepare the evidence inspectors typically ask for.
03Do you provide ongoing compliance support?
Yes. Managed compliance keeps assessments, dashboards and evidence current between audits.
Let's talk
Preparing for an inspection or a new circular?
Tell us your regulator, the framework and your deadline. We'll outline a gap assessment and the evidence you'll need.